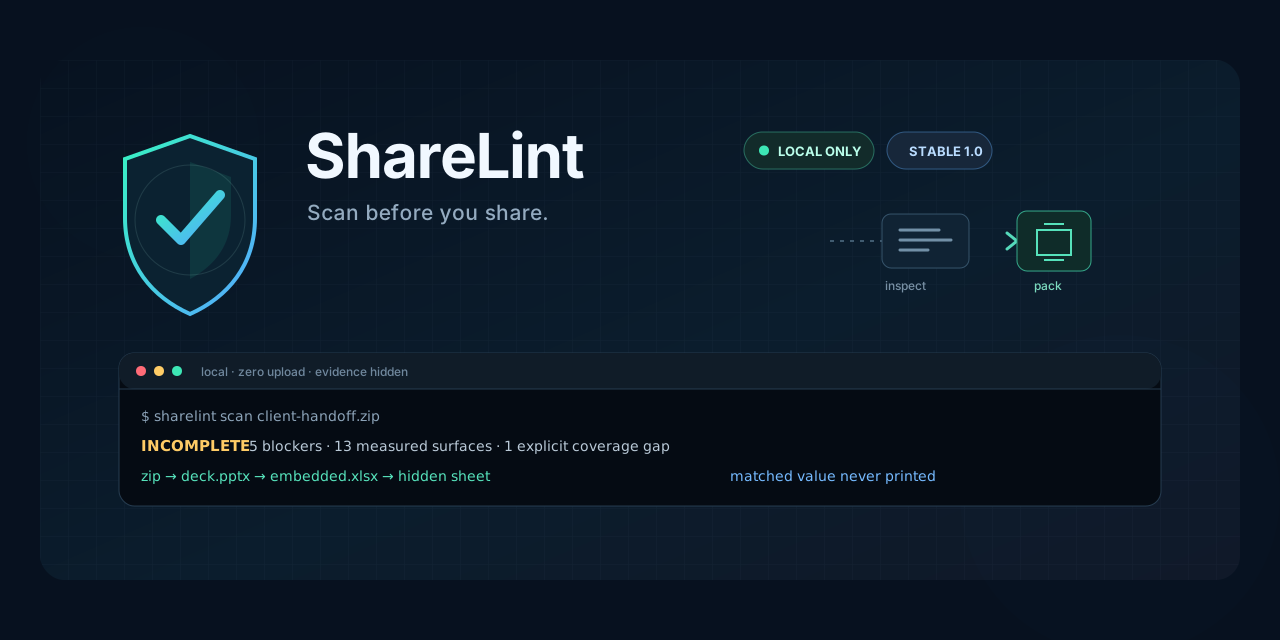
Scan before you share.
A local, fail-closed privacy preflight for files, folders, and nested archives.
Catch secrets, PII, speaker notes, hidden sheets, and location metadata without uploading them.



Quick start · Coverage · Docs · Threat model · 简体中文
The current GitHub release is 2.0.0. This branch contains the original 2.0.0 source and maintained documentation. The 2026-09-14 republication restores the original tag and standalone assets; see what changed since 1.0.
Download a matching archive from a completed GitHub Release. Standalone archives include ShareLint and its Python runtime, so they do not require Python, pip, uv, or pipx on the destination computer. ShareLint 2.0.0 is available for four native targets:
| Computer | Release target |
|---|---|
| x86-64 Linux with glibc | Download Linux |
| 64-bit Windows | Download Windows |
| Intel Mac | Download Intel Mac |
| Apple silicon Mac | Download Apple silicon Mac |
Release v0.1.2 and earlier do not contain these standalone archives. Use only files attached to
a completed release, not ordinary CI artifacts. Download the archive and its same-named .sha256
file, then follow the
verification and first-run instructions.
With Python 3.11+, Git, and pipx installed, select the original 2.0.0 source explicitly:
pipx install 'git+https://github.com/jasonzhang06-source/sharelint.git@v2.0.0'
sharelint --version
sharelint demo
PyPI does not provide 2.0.0. Its original files were deleted and their filenames cannot be reused; the currently available PyPI version is 1.0.0. A normal package-index install or upgrade does not obtain the GitHub 2.0.0 release. Installation uses the network; scanning stays local.
Preview the same synthetic scan as a self-contained local HTML report:
sharelint demo --format html --report sharelint-demo.htmlA standard virtual environment and pip can install the same fixed tag. See the
installation and troubleshooting
guide for standalone archive verification, source installation, PATH fixes, and
externally managed Python environments.
For development, install from a source checkout:
git clone https://github.com/jasonzhang06-source/sharelint.git
cd sharelint
python -m pip install -e .You do not need to switch operating systems to use or develop ShareLint. On Ubuntu, use the Linux
target or the Python package and let CI exercise the native Windows and macOS jobs. A standalone
binary is specific to its listed OS and architecture, so a Windows .exe does not run on Linux;
manual validation of Windows-only host behavior still requires a Windows host.
The Python 3.11+ package is tested on Ubuntu, Windows, and macOS. The standalone matrix covers the four native targets listed above. Check the CI result for the exact commit or release you use. A configured target does not imply that every filesystem, OS version, shell, locale, or security policy has been verified.
Writing reports, bundles, archives, and receipts requires hard-link support in the destination filesystem so ShareLint can preserve its no-overwrite contract. See platform support for the validation matrix, Windows notes, and filesystem limitations.
ShareLint 2.0. Create a reviewable handoff plan, then pack only if source and policy still match. New receipt schema 2.0.0 replaces filenames with ZIP entry indices; native scan reports remain 1.0.0. Read the migration guide. PDF pages and image pixels are not OCR-scanned; incomplete coverage still blocks
pack.
You are about to send a ZIP. The code is clean, but the deck still has speaker notes, the workbook contains a very-hidden sheet, the PDF names its author, and an image records a location. Git-focused secret scanners do not see that entire boundary. ShareLint does.
It recursively follows a finding through nested containers, hides the matched value in every report,
and says when a surface was only partially inspected. Its pack command creates a deterministic ZIP
only after the configured policy and coverage checks pass, then reopens and rescans the output.
Most tools inspect one layer of a handoff. ShareLint treats the selected file, directory, and every supported nested container as one disclosure boundary:
| Approach | Strong at | What ShareLint adds |
|---|---|---|
| Repository secret scanning | Credentials in source and history | Office/PDF/image surfaces, filenames, and nested delivery bundles |
| Metadata inspection or cleanup | Individual format fields | Cross-format provenance, content rules, and an explicit coverage ledger |
| Hosted DLP | Organization-wide policy and managed channels | A zero-upload personal preflight with no service or account |
| Manual ZIP review | Human context | Repeatable limits, masked evidence, output rescan, and hash-bound receipts |
It is intentionally composable with those controls rather than a replacement for all of them.
The demo builds a disposable, entirely synthetic handoff bundle in a temporary directory. Its console output starts with a banner confirming that the data is synthetic and no personal files were read. It shows nested Office content, PDF metadata, active content, redacted evidence, and an explicit PDF coverage gap without touching your files. Abridged Linux output (filesystem metadata surface counts may vary by platform):
SYNTHETIC DEMO · generated sample only
No personal files were read; this run scanned only files created by ShareLint.

ShareLint 2.0.0 · local privacy preflight
INCOMPLETE · 5 policy-blocking finding(s) · 9 total · 14 surface(s)
Coverage · 13 scanned · 1 partial · 0 skipped · 0 error(s)

CRITICAL SL.SECRET.AWS_ACCESS_KEY · AWS access key identifier
         client-handoff.zip -> deck.pptx -> ppt/embeddings/clients.xlsx
         evidence <secret:20 chars> [report-scoped fingerprint]

Coverage gaps
  PARTIAL client-handoff.zip -> report.pdf · rendered-page OCR is not enabled

Original untouched · 0 bytes uploaded · matched values hidden
Incomplete means one or more listed surfaces were not fully inspected.
Found it useful? Star ShareLint, report a false positive, or request a format.
Use a repeatable policy:
sharelint scan ./client-handoff --profile public
sharelint config init -o sharelint.toml
sharelint config show --config sharelint.toml --profile client
See the configuration guide. Configuration is explicit, never auto-discovered inside untrusted input.
Scan a file, directory, ZIP, or Office document:
sharelint scan ./client-handoffWrite a machine-readable report or a static HTML review:
sharelint scan ./client-handoff --format json  -o sharelint.json
sharelint scan ./client-handoff --format sarif -o sharelint.sarif
sharelint scan ./client-handoff --format html  -o sharelint.html
Report outputs are owner-only where supported, never overwrite an existing path, and must sit
outside a scanned directory. demo --report follows the same rule; demo -o writes the reusable
synthetic ZIP bundle and also refuses to overwrite an existing path.
Make coverage gaps fail a normal scan in automation:
sharelint scan ./client-handoff --strict --fail-on highCreate a share bundle only if it passes the fail-closed gate:
sharelint pack ./approved-files -o release.zipOn success, this writes release.zip, the minimized receipt
release.zip.sharelint.json, and its exact companion report
release.zip.sharelint.report.json. The receipt binds the output hash, policy, measured coverage,
and companion report digest. On failure, no archive is published. An explicit
--receipt blocked.json may write blocked.json plus blocked.report.json for the blocked attempt;
it is never a success receipt. Companion reports include masked findings and contextual filenames,
so protect them as sensitive records even though matched values remain hidden. Successful receipts
use ZIP entry indices instead of repeating filenames and should still be protected.
pack always rejects partial, skipped, or errored coverage. There is deliberately no bypass flag:
a pack receipt is only meaningful when every required surface was inspected.
Discover the current rule set from the installed checkout:
sharelint rules
sharelint explain SL.OFFICE.NOTES| Code | Meaning |
|---|---|
0 |
Command completed and the selected gate did not block. |
1 |
Findings met the threshold, strict coverage failed, or pack was blocked. |
2 |
Invalid usage, unreadable input, or another operational error. |
130 |
The user interrupted the command. Review any completed outputs before retrying. |
sharelint demo intentionally returns 0 after rendering its synthetic blocked example.
The console and HTML report use REVIEW when a completed scan found something below the selected
--fail-on threshold. That is a prompt for human review, not a blocking verdict: the exit code is
still 0, and JSON/SARIF keep summary.verdict: "pass" for the stable automation contract. PASS
means no findings were retained; neither label is a guarantee that the input is safe.
| Surface | Current inspection | Coverage semantics |
|---|---|---|
| Directories | Stable recursive walk, path/name checks, regular files | Symlinks are not followed; skipped or unsupported entries stay visible. |
| ZIP archives | Bounded in-memory member inspection, archive/entry comments, extra fields, nested archives, path traversal, links, encryption, duplicates, bomb limits | Members are never extracted to disk. A limit, unreadable member, or unknown extra-field type is a gap. |
| Office Open XML | DOCX/XLSX/PPTX properties, comments, revisions, hidden text/sheets/slides, notes, external relationships, macros, custom XML, previews, embedded objects | OOXML receives the same archive limits; embedded packages retain their full source chain. |
| Static metadata, active-content markers, attachments, encryption, and incremental history | Incomplete: rendered pages are not OCR-scanned and no viewer is invoked. | |
| Images | JPEG/PNG/WebP/TIFF metadata, including identity, device, text, and GPS fields where supported | Incomplete: pixels are not OCR-scanned; “metadata scanned” does not mean “image content scanned.” |
| Text | Common credentials, private-key markers, emails, US SSNs, payment cards, and revealing local paths | Pattern-based detection can have false positives and false negatives. |
Run sharelint rules for the installed rule registry and read
Rules and identifiers for stability and severity semantics.
files / folders / nested containers
                 │
                 ▼
        bounded local traversal
                 │
       ┌─────────┼──────────┐
       ▼         ▼          ▼
    secrets   document   coverage
      + PII    surfaces     gaps
       └─────────┼──────────┘
                 ▼
       privacy-safe findings
                 │
          scan ──┴── pack gate
                         │ pass only
                         ▼
               deterministic ZIP
                  + hash receipt
                  + output rescan
The core scan path has no network feature, telemetry, or runtime dependency outside Python's standard library. It does not execute macros or JavaScript, invoke Office/PDF applications, follow external relationships, or extract archive members to disk.
The architecture guide maps these guarantees to module boundaries and documents safe extension points for contributors.
Findings carry a nested logical source chain such as:
handoff.zip -> deck.pptx -> ppt/embeddings/customers.xlsx -> xl/workbook.xml
Matched evidence is reduced immediately to a type-aware mask and a keyed, report-scoped fingerprint. The ephemeral HMAC key is never serialized, so the fingerprint cannot be used as a stable cross-report identifier. Reports are still sensitive because filenames, structure, finding types, and counts can reveal context.
ShareLint is a preflight, not a proof system. A pass means only that no configured blocker was found on the surfaces listed in that report under that policy.
- It cannot guarantee that a bundle is safe, anonymous, compliant, or free of sensitive data.
- It does not currently OCR PDF pages or image pixels.
- It does not sanitize or modify originals; fix issues in a share-specific copy, then rescan.
- It cannot determine whether a detected credential is live or whether personal data was intended.
- Unsupported, encrypted, malformed, or budget-limited content remains a visible coverage gap.
The security boundary and residual risks are documented in the
threat model. Machine-output consumers should use the
report and receipt contract, not parse console text.
JSON Schema files for automated validation live in schemas/.
sharelint verify release.zip --receipt release.zip.sharelint.json --report release.zip.sharelint.report.jsonThe verifier checks exact report/archive bytes, recomputed report summaries, recorded policy settings, and ZIP file manifests. It does not upload or extract files. Integrity is not a signature, producer authentication, a new privacy scan, or a guarantee of safe sharing. See the verification contract for blocked receipts, independent digest pinning, budgets, and exit codes.
sharelint diff before.json after.json
sharelint diff before.json after.json --format html -o comparison.html
Report comparison checks rule/severity counts and coverage. It flags increased blockers, incomplete coverage, reduced inspection, and changed settings for review. It never treats report-scoped fingerprints as stable evidence IDs, and fewer findings do not prove a particular issue was fixed. See the comparison guide.
sharelint plan create ./handoff -o handoff.plan.json
sharelint plan inspect handoff.plan.json
sharelint pack ./handoff -o delivery.zip --plan handoff.plan.json
Packing repeats all strict checks and rejects changed source, policy, or scan snapshots. A plan is a private review record, not approval or a signature. See handoff plans.
ShareLint adds explicit policy profiles, offline receipt verification, report comparison, and reviewable handoff plans to the scanning/packaging workflow. The maintenance priority is synthetic regression tests, conservative coverage, and compatibility. Local OCR, policy exceptions, pre-send hooks, and a desktop interface remain future work. See the roadmap.
The project stays useful by keeping three promises measurable: input remains local, evidence remains hidden, and incomplete coverage never masquerades as a clean scan.
The most useful early feedback is a real sharing workflow described with synthetic data: a format that ShareLint cannot inspect yet, a false positive that can be reproduced safely, or a report that was hard to act on. Open a focused feature request or bug report. If ShareLint fits a problem you care about, starring the repository helps more people discover it.
Issues and pull requests are welcome, especially for narrowly scoped format coverage, synthetic regression fixtures, false-positive reductions, and hostile-input tests. Start with CONTRIBUTING.md and never attach real secrets or personal documents.
Report a possible vulnerability privately through GitHub's Security → Report a vulnerability flow, as described in SECURITY.md. General help is covered by SUPPORT.md; project decisions follow GOVERNANCE.md.
MIT © ShareLint contributors.